Inside Telegram’s Underground “Clouds”: How Exfiltrated Data Gets Packaged and Sold
Telegram “cloud” channels sell infostealer logs, combo lists and server logins in bulk, and much of the data is recycled under new names. This article shows what the channels offer, the three seller tiers from malware operators to mass resellers, how the data moves from infection to channel, and which mitigations help.
WebThreat Research · Published · 4 min read
Tiered reselling, hacking channels, and endless stolen credentials: take a look at the darker side of Telegram’s marketplace.
1. The Rise of Telegram “Clouds”
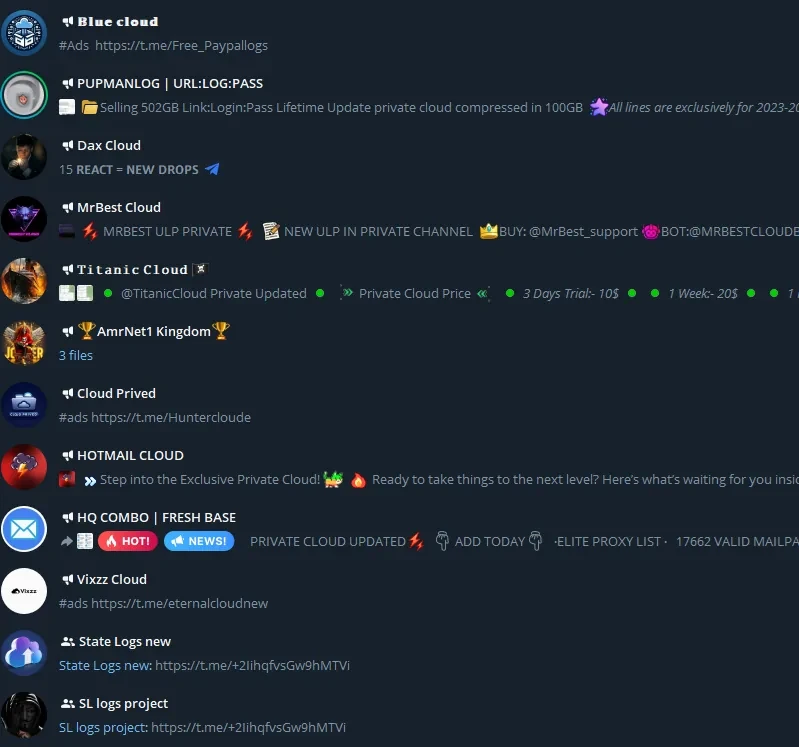
From “Blue Cloud” and “Titanic Cloud” to “PUPMANLOG” and “TrustCloud,” Telegram hosts countless groups and channels claiming to offer massive “clouds” of stolen data. Some label them “ULP” (Unlimited Private Lists), while others refer to them as logs or combos. Each claims to have fresh content from 2023 to 2024, though reality often tells a different story.
Why Telegram? Mainly because it’s convenient, has large-group functionality, and offers a quick pivot if channels get banned. Combine that with user-friendly smartphone apps and the ability to create multiple aliases, and you have a near-perfect environment for illicit data trade.
2. Screenshots: Telegram Clouds in Action
3. What’s Actually Being Sold?
In these “clouds,” you’ll find:
- Streaming Service Credentials (e.g., Netflix, Hulu, Disney+)
- Email/SMTP Access (used for spam or more phishing)
- Web Hosting Logins (cPanel, phpMyAdmin, WordPress, Joomla, etc.)
- SSH/Root/RDP (server control for cryptomining, web shell deployment, or data theft)
- Plain Combo Lists (username:password pairs for credential stuffing across multiple sites)
Each cloud channel claims its data is “fresh,” “private,” or “unpublished,” but in practice, they often recycle and rename logs from other groups.
4. The Tiered Market Structure
Tier 1: Originators
- Malware operators. They run RATs, keyloggers, or infostealers that directly collect user credentials.
Tier 2: Curators
- Buy raw logs from Tier 1, remove duplicates, maybe verify or categorize them, and rebrand as “ULP” or “private combos.”
Tier 3: Mass Resellers
- Often the loudest and easiest to find, spamming Telegram with quick deals and cut-rate subscriptions, but offering heavily duplicated data.
5. Marketing Tactics: The Illusion of Exclusivity
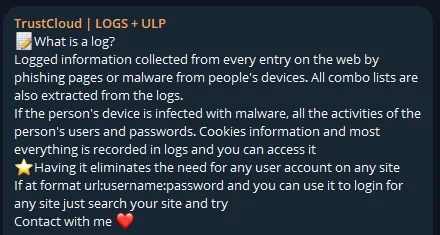
Take the TrustCloud pitch as an example: they highlight how logs capture everything from browser cookies to usernames and passwords, making it effortless to hop between sites using the same stolen credentials. Other channels throw in emojis, flashy formatting, and “trial deals” (like $10 for 3 days) to lure new buyers.
While Telegram channels can boast about having “lifetime updates” and “compressing 100GB” of data, it’s really just a hustle: the same logs can appear under different banners a week later.
6. Data Flow: From Infection to Telegram Channels
Malware Infection
- The victim runs an infostealer. Everything typed or auto-filled (including cookies) is logged.
C2 Server Aggregation
- The stolen credentials are uploaded to a malware operator’s command-and-control server.
Packaging & Sale
- Logs are zipped and sold privately (Tier 1 → Tier 2). Tier 2 might parse them into domain-labeled combos.
Telegram “Cloud” Distribution
- Tier 3 mass resellers push them into multiple channels with enticing claims.
Final Exploitation
- Buyers target vulnerable accounts or resell the logs yet again, perpetuating the cycle.
7. Real-World Consequences
- Account Takeover: Netflix or Hulu hacks might seem minor, but many people reuse passwords, opening the door to more serious breaches.
- Business Impact: cPanel or SSH credentials can expose entire corporate networks.
- Continuous Phishing: With stolen SMTP or email logins, criminals can blast out even more phishing campaigns.
- Identity Theft: Some logs contain personal details well beyond just usernames and passwords.
8. Mitigations and Best Practices
Use Unique Passwords + MFA
- A stolen Netflix password is less harmful if it’s not the same as your email or bank.
Monitor for Leaks
- Companies can track if corporate credentials appear in these “clouds,” prompting rapid account resets.
Employee Security Training
- Proper awareness reduces the likelihood of malware infections in the first place.
Collaboration with Law Enforcement
- Reporting the channel handles and admin IDs can help sometimes, though these groups often reappear fast.
9. Conclusion: A Peek Behind Telegram’s Curtain
As the snapshots show, Telegram “cloud” channels are effectively a spammy, yet alarmingly efficient clearinghouse for stolen credentials. They thrive on a tiered system: from the hackers controlling malware at the top, to the mass resellers at the bottom peddling “fresh” (but often recycled) credentials.
By understanding how these “clouds” package and market exfiltrated data, security professionals and the public at large can better anticipate attacks and reinforce their own defenses. Ultimately, the same stolen Netflix log might resurface many times under various names, but the impact remains real if people don’t lock down their accounts.
Note: This article is based on real-life observations of public Telegram groups. None of the details provided here are intended to encourage illegal activity. Always adhere to your local laws and ethical guidelines when researching or investigating these channels.
First published on Medium on 7 January 2025.
Terms used in this article
Related
Stolen-data ecosystem and actors
php2shell: the two critical PHP flaws and what to do now
php2shell is the name for two critical flaws in the PHP runtime, CVE-2026-109618 and CVE-2026-109619, both rated CVSS v4.0 9.2. They can allow unauthenticated r...
Stolen-data ecosystem and actors
Case Study: Unveiling 642,639 Government Credential Leaks Across 192 Countries
The Global Government Credential Leaks Study found 642,639 government credential leaks across 192 countries, collected from 83 dark web and Telegram sources. Br...
Stolen-data ecosystem and actors
FBI Crushes Nulled & Cracked.io, but Cybercriminals Already Have a Backup Plan
After the January 2025 seizure of the forums Nulled.to and Cracked.io, cybercriminals are shifting stolen-data trading to Telegram “clouds”. The article explain...
See your leadership's exposure
CEM finds your executives from your company name, checks them against breach corpora and leak databases, and scores each person from 0 to 100.