The Invisible Threat of Exfiltrated Data: Unmasking the Underworld of Telegram-Based Data Sales
Telegram channels are used to list and sell exfiltrated data and access to compromised machines. The article describes the sales workflow from C2 server to listing to payment, the difference between direct access and control panels, indicators of compromise to watch for, and defensive measures for organizations.
WebThreat Research · Published · 7 min read
In the ever-evolving landscape of cybersecurity, threats often lurk in the shadows, evading traditional defenses and exploiting overlooked vulnerabilities. Among these silent dangers, the exfiltration and sale of data via platforms like Telegram represent a burgeoning menace. This article delves deep into the clandestine operations of Telegram hacking cloud chats, the marketplace dynamics of data exfiltration, and the sophisticated methods employed by threat actors to exploit compromised systems.
1. The Dark Nexus: Telegram as a Marketplace for Exfiltrated Data
Telegram, renowned for its robust encryption and user-friendly interface, has inadvertently become a hub for cybercriminal activities. Its blend of privacy features and widespread adoption makes it an ideal platform for selling and distributing exfiltrated data. Threat actors leverage Telegram’s anonymity to facilitate transactions, share access to compromised systems, and distribute malicious tools without immediate detection.
Exhibit A: A recent investigation uncovered multiple Telegram channels explicitly dedicated to selling access to compromised machines. These channels offer a range of services, from direct access to specific domains or email accounts to broader control over entire networks.
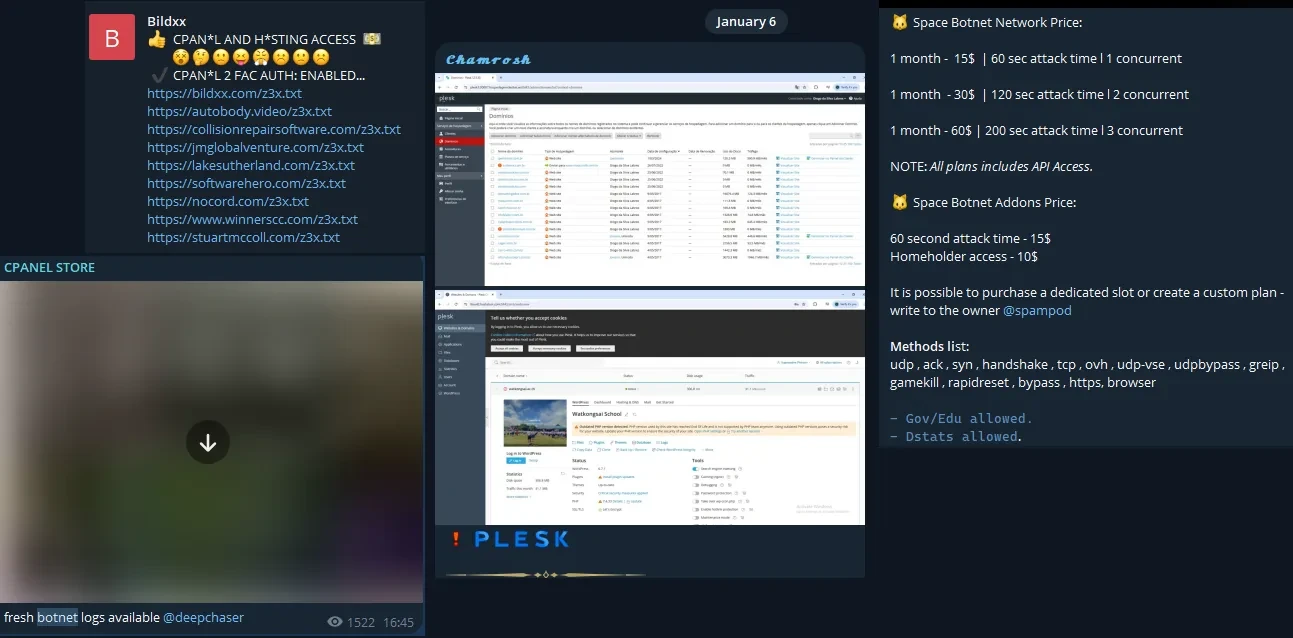
Key Features Enabling This Ecosystem:
- End-to-End Encryption: Ensures that communications between buyers and sellers remain private.
- Anonymous Account Creation: Allows users to operate without revealing their identities.
- Bot Integration: Automates transactions and manages listings, enhancing operational efficiency.
2. Anatomy of a Telegram-Based Data Sale
Understanding the workflow of data exfiltration sales on Telegram provides insight into the scale and sophistication of these operations.
Step 1: Data Exfiltration from C2 Servers
Command and Control (C2) servers act as the nerve centers for orchestrating cyberattacks. Once compromised, these servers facilitate the extraction of sensitive data using infostealers, logging tools, and brute-force techniques. The exfiltrated data is then packaged for distribution.
Step 2: Listing on Telegram Channels
Cybercriminals list their offerings on specialized Telegram channels. Listings typically include:
- Type of Data: Emails, passwords, financial records, intellectual property, etc.
- Access Level: Read-only access, administrative privileges, full system control.
- Price Points: Vary based on the data’s sensitivity and volume.
Step 3: Transaction and Delivery
Using Telegram bots, transactions are conducted seamlessly. Buyers make payments via cryptocurrencies, and upon confirmation, access credentials or data dumps are provided through secure file-sharing methods.
3. Direct Access vs. Indirect Access: The Spectrum of Control
Cybercriminal marketplaces on Telegram offer varying degrees of access to compromised systems, each with its own implications for organizational security.
Direct Access to Compromised Machines
Some sellers provide live access to infected machines. Buyers can:
- Browse Domains or Emails: Access specific user accounts or domains to harvest information.
- Execute Commands: Perform actions that can further compromise the network or exfiltrate additional data.
- Install Additional Malware: Enhance control over the compromised system for prolonged access.
Indirect Access through Control Panels
Other listings offer access to control panels that manage multiple compromised systems. This method allows buyers to:
- Scale Operations: Manage numerous compromised machines simultaneously.
- Automate Tasks: Deploy malware or conduct data exfiltration across a fleet of systems with minimal manual intervention.
- Monitor Activities: Track the effectiveness of their malicious campaigns as they run.
4. The Unseen Battle: Red Teamers vs. Telegram-Based Threats
Even the most comprehensive attack surface mapping and red teaming exercises can fall short against the stealthy operations facilitated by Telegram-based data sales.
Limitations of Traditional Red Teaming:
- Dynamic Threat Landscape: Rapidly evolving tactics employed by cybercriminals on platforms like Telegram can outpace traditional defense mechanisms.
- Insider Threats: Malicious actors leveraging compromised internal systems can bypass external security measures entirely.
- Sophisticated Evasion Techniques: Use of encrypted channels and anonymization tools makes detection and attribution challenging.
Identifying the Invisible: Indicators of Compromise (IoCs)
The subtle signs of a Telegram-based data breach often manifest during lateral movements within the network:
- Unusual Network Traffic: Unexpected outbound connections to unknown Telegram servers.
- Anomalous User Behavior: Legitimate user accounts exhibiting unauthorized access patterns or executing unfamiliar commands.
- Unauthorized Software Installations: Detection of malware or infostealers that facilitate data exfiltration.
5. Mitigating the Telegram Threat: Strategic Defense Mechanisms
To safeguard against the invisible threat of exfiltrated data sold on Telegram, organizations must adopt a multi-faceted defense strategy that encompasses prevention, detection, and response.
Automated Monitoring of Network Traffic
Implement advanced network monitoring tools that can identify and flag unusual traffic patterns associated with Telegram-based exfiltration activities.
Endpoint Detection and Response (EDR) Solutions
Deploy EDR solutions that can detect and respond to malicious activities on endpoints, including unauthorized access attempts and malware installations.
User Behavior Analytics (UBA)
Leverage UBA to establish baselines for normal user activities and detect deviations indicative of compromised accounts or insider threats.
Regular Security Audits and Penetration Testing
Conduct frequent security assessments to identify and remediate vulnerabilities that could be exploited for data exfiltration.
Employee Training and Awareness Programs
Educate employees about the risks associated with compromised systems and the importance of adhering to security protocols to prevent lateral movements.
6. Case Study: The Silent Breach of a Financial Institution
In early 2024, a major financial institution fell victim to a sophisticated Telegram-based data exfiltration campaign. Despite robust perimeter defenses and regular security audits, the attackers exploited an overlooked vulnerability within the organization’s internal network.
Timeline of Events:
- Initial Compromise: Attackers infiltrated the network through a phishing campaign targeting administrative staff.
- Establishing C2 Communication: Malware installed on compromised systems established encrypted communication channels with Telegram-based C2 servers.
- Data Exfiltration: Sensitive financial data was systematically extracted and uploaded to Telegram channels for sale.
- Detection and Response: Unusual outbound traffic patterns were detected by the organization’s EDR system, triggering an incident response protocol.
- Containment and Recovery: Rapid containment measures were implemented, including isolating affected systems and conducting a comprehensive forensic analysis.
Lessons Learned:
- Importance of Internal Monitoring: External defenses alone are insufficient; continuous monitoring of internal network activities is crucial.
- Proactive Threat Hunting: Regular threat hunting exercises can identify latent threats before they escalate.
- Comprehensive Incident Response Plans: Well-defined and practiced response plans enable swift action to mitigate breaches effectively.
7. The Future of Data Exfiltration: Evolving Tactics and Emerging Threats
As cybersecurity defenses become more sophisticated, so too do the tactics of threat actors. The future landscape of data exfiltration will likely feature:
AI-Driven Attacks
Artificial Intelligence (AI) and Machine Learning (ML) will enable more precise and adaptive attack strategies, allowing cybercriminals to bypass traditional defenses with ease.
Decentralized Marketplaces
Blockchain technology may facilitate the creation of decentralized marketplaces for data sales, making it even more challenging to track and dismantle these illicit operations.
Advanced Steganography
The use of steganographic techniques to hide exfiltrated data within innocuous files or communications will complicate detection efforts.
Supply Chain Exploits
Targeting third-party vendors and supply chains will provide attackers with indirect access to multiple organizations, amplifying the impact of data breaches.
8. Proactive Measures: Building Resilient Defenses Against Telegram-Based Threats
To stay ahead of the curve, organizations must adopt proactive measures that anticipate and neutralize emerging threats from platforms like Telegram.
Implement Zero Trust Architecture
Adopt a Zero Trust approach, ensuring that every access request is authenticated, authorized, and encrypted, regardless of its origin within or outside the network.
Enhance Threat Intelligence Sharing
Collaborate with industry peers and threat intelligence communities to stay informed about the latest tactics, techniques, and procedures (TTPs) employed by cybercriminals.
Invest in Advanced Analytics
Utilize big data analytics and AI-driven tools to process vast amounts of security data, identifying patterns and anomalies that may indicate sophisticated attacks.
Strengthen Access Controls
Enforce stringent access controls and privilege management to minimize the risk of unauthorized access and lateral movement within the network.
Continuous Improvement and Adaptation
Regularly update and refine security policies and technologies to adapt to the evolving threat landscape, ensuring sustained resilience against emerging dangers.
9. Final Thoughts: Navigating the Shadows with Vigilance and Innovation
The invisible threat of exfiltrated data sold on Telegram underscores the imperative for organizations to adopt a holistic and forward-thinking approach to cybersecurity. As threat actors continue to exploit sophisticated platforms and techniques, the onus is on defenders to innovate, adapt, and remain ever vigilant.
Key Takeaways:
- Visibility is Crucial: Achieving comprehensive visibility into network activities is essential for early detection and response.
- Collaboration Enhances Security: Sharing intelligence and best practices within the cybersecurity community strengthens collective defenses.
- Embrace Technological Advancements: Leveraging cutting-edge technologies empowers organizations to anticipate and counteract evolving threats effectively.
Note: The insights shared in this article are intended for educational and awareness purposes. Always adhere to legal frameworks and ethical guidelines in cybersecurity practices and research.
First published on Medium on 18 January 2025.
Terms used in this article
Related
Stolen-data ecosystem and actors
php2shell: the two critical PHP flaws and what to do now
php2shell is the name for two critical flaws in the PHP runtime, CVE-2026-109618 and CVE-2026-109619, both rated CVSS v4.0 9.2. They can allow unauthenticated r...
Stolen-data ecosystem and actors
Case Study: Unveiling 642,639 Government Credential Leaks Across 192 Countries
The Global Government Credential Leaks Study found 642,639 government credential leaks across 192 countries, collected from 83 dark web and Telegram sources. Br...
Stolen-data ecosystem and actors
FBI Crushes Nulled & Cracked.io, but Cybercriminals Already Have a Backup Plan
After the January 2025 seizure of the forums Nulled.to and Cracked.io, cybercriminals are shifting stolen-data trading to Telegram “clouds”. The article explain...
See your leadership's exposure
CEM finds your executives from your company name, checks them against breach corpora and leak databases, and scores each person from 0 to 100.